About
Security leadership forged where the stakes are systemic.
CISO Advisory Group brings senior cybersecurity leadership to organisations that need it most — whether you are scaling rapidly, navigating a complex regulatory landscape or facing risks your team has not met before.
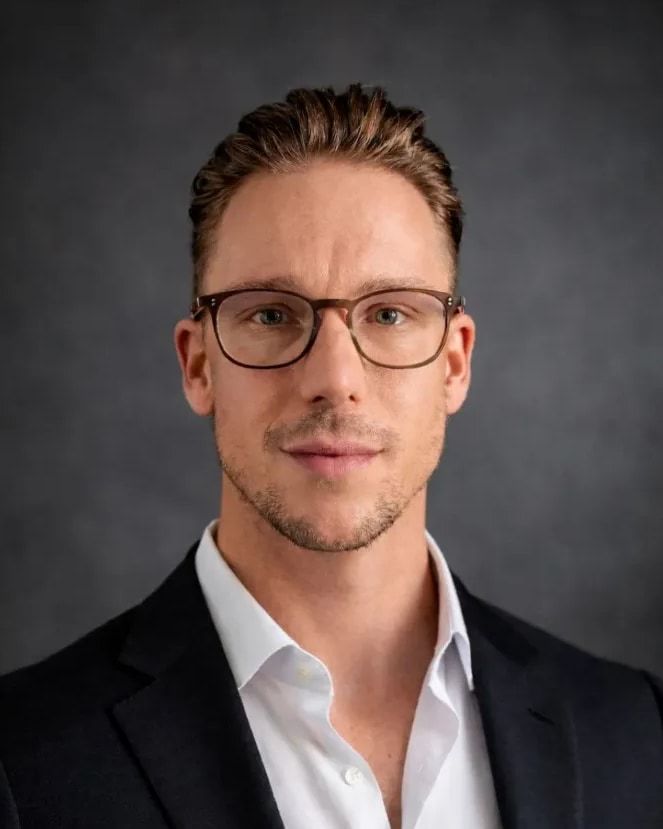
Our principal
Aidan Tolson
Principal CISO Advisor
Our principal has spent more than two decades leading security at the highest levels of global finance and critical national infrastructure, including accountability for a £300m annual security change budget and a security portfolio spanning more than 50 countries.
That depth of experience is what we bring to every engagement — applied practically to your environment, your risks and your business objectives. We are not a consultancy that produces reports and moves on. We embed, we own outcomes and we stay until the job is done.
Beyond direct engagements, our principal has presented original research on AI security and post-quantum readiness to Tier 1 financial institution leadership teams, and has delivered executive and practitioner training across identity and access management, privileged access, GRC, AI security and post-quantum readiness.
Career includes
- HSBC
- JPMorgan Chase
- UK Government
- Critical National Infrastructure
- Annual security change budget led
- £300m
- Years of executive cybersecurity leadership
- 20+
- Countries in a single global security portfolio
- 50+
How we’re different
Three ways security transformation gets delivered. Only one keeps the person who built the trust accountable for the outcome.
-
The Big Four model
A senior partner sells the vision. Once the statement of work is signed, delivery passes to graduates and junior consultants. The cost stays senior-level. The delivery doesn’t.
-
The staffing model
Reliable delivery resource against a defined scope. No strategic ownership, no governance and no one accountable for whether the engagement actually moves the needle.
-
Our model
The senior leader who builds the credibility stays engaged for the life of the engagement — owning governance and outcomes — while directing a vetted bench of architects, engineers, project managers and analysts against the plan.
Principles
What you can hold us to.
- 01
Senior from day one
The person who scopes the work leads it and stays accountable for the outcome. No hand-off to a junior team once the contract is signed.
- 02
Vendor-independent
We do not resell third-party security products or take referral fees. Our recommendations are shaped by your risk, not a partner programme.
- 03
Outcomes, not reports
Every engagement ends with something your teams can act on and your board can fund — not a document that sits on a shelf.
- 04
Confidential by default
We work with regulated organisations on sensitive problems. Discretion is not an add-on; it is how we operate.
Selected engagements
Proof, not promises. Anonymised by design.
-
Tier 1 financial market infrastructure
Target operating model & agentic AI transformation roadmap
Engaged to redesign the security operating model for a Tier 1 global exchange group, running a privileged access management uplift in parallel and building the target operating model and delivery roadmap for the organisation’s first agentic AI deployments.
-
Tier 1 global bank
Strategy and investment portfolio at global scale
Designed and executed the cybersecurity strategy and investment roadmap for a Tier 1 global bank across more than 50 countries, while embedding a leaner, more efficient operating model.
-
High-growth SaaS
Rebuilding a security function inherited from tooling-led delivery
Took over as fractional CISO from a tooling-led buildout that had deployed security products without the operational maturity to run them. Stood up SOC coverage, DLP, a risk management and GRC programme, control assurance and a board-level cyber strategy from the ground up.
-
Enterprise SaaS platform
FedRAMP Rev5 & 20x readiness
Leading a fast-scaling SaaS platform through FedRAMP Rev5 authorisation to submission milestone, while standing up SOC coverage, vulnerability management, a GRC programme and continuous monitoring to meet FedRAMP 20x readiness requirements.
CISO Advisory Group Limited · Company No. 16785256 · Registered in England & Wales
Start with a confidential conversation.
Sixty minutes with a senior practitioner. No sales team, no obligation — just a candid view of where you stand and what to do first.